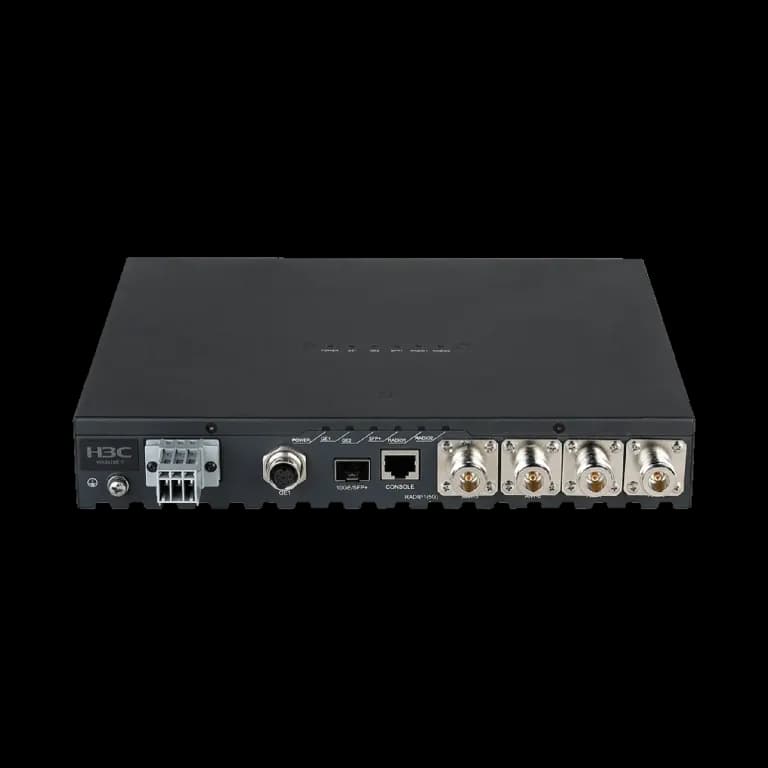
H3C WA6628E-T Wi-Fi 6 Rail Transit Access Point
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
Price on Request
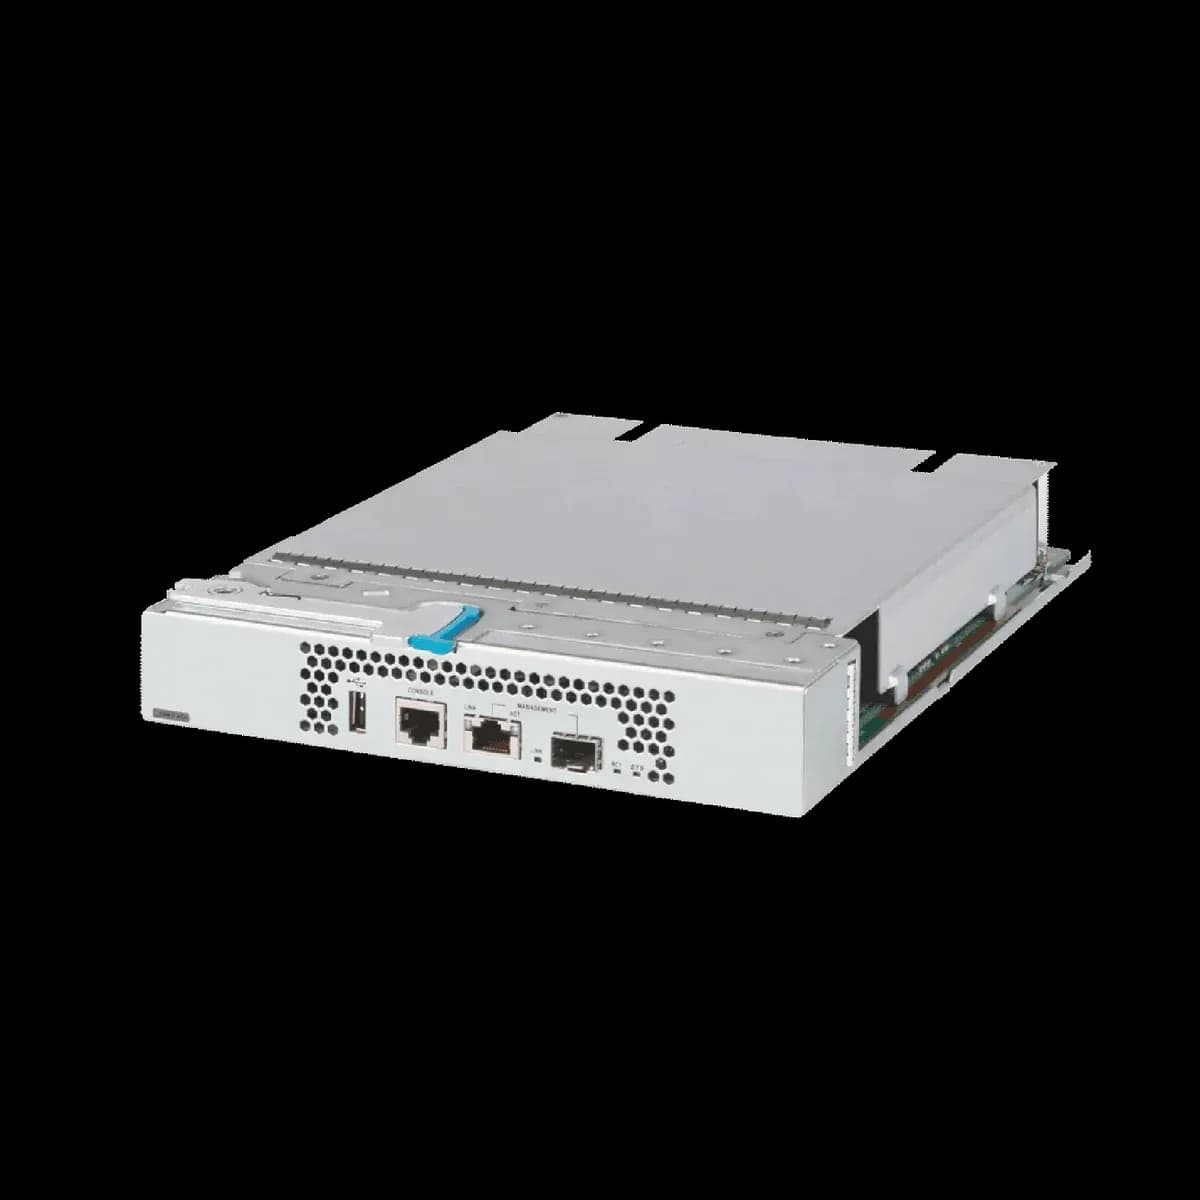
A next-generation firewall card that slots into H3C switches and routers, adding security without extra appliances.
Island-wide delivery to all 25 districts
| Compatible devices | H3C S5130, S5560, S5560X, S5590, S5800, S6520X, S6800, S6900, S7500E, S7500X, S7500X-G, S7600, S7600-X, S10500, S10500X, S10500X-G, S12500-S, S12500-X, S12500G-AF, S12500X-AF, and S12500F-AF switches CR16000-F routers |
|---|---|
| Interfaces | One configuration interface (console) One Ethernet management interface (RJ-45) |
| Temperature | Operating: 0 to 45 °C Storage: -40 to 70 °C |
| Hot swapping | Supported |
| Operating mode | Route, transparent, and hybrid |
| AAA services | Portal authentication RADIUS authentication HWTACACS authentication PKI/CA (X.509 format) authentication Domain authentication CHAP authentication PAP authentication |
| Firewall | SOP virtual firewall technologies, supporting full virtualization of CPU, memory, and storage resources Security zone allocation Protection against malicious attacks, such as land, smurf, fraggle, ping of death, teardrop, IP spoofing, IP fragmentation, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, address/port scanning, SYN flood, ICMP flood, UDP flood, and DNS query flood Basic and advanced ACLs Time range-based ACL User-based and application-based access control ASPF application layer packet filtering Static and dynamic denylists MAC-IP binding MAC-based ACL 802.1Q V |
| Anti-virus | Signature-based virus detection Manual and automatic upgrade for the signature database Stream-based processing Virus detection based on HTTP, FTP, SMTP, and POP3 Virus types include Backdoor, Email-Worm, IM-Worm, P2P-Worm, Trojan, AdWare, and Virus Virus logs and reports |
| Deep intrusion prevention | Prevention against common attacks such as hacker, worm/virus, Trojan, malicious code, spyware/adware, DoS/DDoS, buffer overflow, SQL injection, and IDS/IPS bypass Attack signature categories (based on attack types and target systems) and severity levels (including high, medium, low, and notification) Manual and automatic upgrade for the attack signature database (TFTP and HTTP) P2P/IM traffic identification and control |
| Email/webpage/application layer filtering | Email filtering: SMTP email address filtering, Email subject/content/attachment filtering Webpage filtering: HTTP URL/content filtering Application layer filtering: Java Blocking, ActiveX Blocking, SQL injection attack prevention |
| NAT | Many-to-one NAT, which maps multiple internal addresses to one public address Many-to-many NAT, which maps multiple internal addresses to multiple public addresses One-to-one NAT, which maps one internal address to one public address NAT of both source address and destination address External hosts access to internal servers Internal address to public interface address mapping NAT support for DNS Setting effective period for NAT NAT ALGs, including DNS, FTP, H.323, ILS, MSN, NBT, PPTP, and SIP |
| VPN | L2TP VPN, IPSec VPN, GRE VPN, SSL VPN |
| IPv6 | IPv6 status firewall IPv6 attack protection IPv6 protocol: IPv6 forwarding, ICMPv6, PMTU, Ping6, DNS6, TraceRT6, Telnet6, DHCPv6 Client, and DHCPv6 Relay IPv6 routing: RIPng, OSPFv3, BGP4+, static routing, policy-based routing, PIM-SM, and PIM-DM IPv6 security: NAT-PT, IPv6 Tunnel, IPv6 Packet Filter, Radius, IPv6 zone pair policies, IPv6 connection limit |
| High availability | Stateful failover (Active/Active and Active/Backup modes) Configuration synchronization of two firewalls |
| High maintainability | Configuration management at the CLI Remote management through Web GUI Device management through H3C SSM Security Management Center SNMPv3, compatible with SNMPv2 and SNMPv1 Intelligent security policy |
| Environmental protection and certification | European RoHS environmental certification |
| Operation modes | Route, transparent, and hybrid |
| AAA | Portal authentication RADIUS authentication HWTACACS authentication PKI/CA (X.509 format) authentication Domain authentication CHAP authentication PAP authentication |
| Antivirus | Signature-based virus detection Manual and automatic upgrade for the signature database Stream-based processing Virus detection based on HTTP, FTP, SMTP, and POP3 Virus types include Backdoor, Email-Worm, IM-Worm, P2P-Worm, Trojan, AdWare, and Virus Virus logs and reports |
| Asset-security analysis | Botnet Analysis: analyses all security logs related to botnets and supports displaying information about hosts that might be zombie hosts, including zombie host IP and peer IP Security Analysis: analyzes health status of hosts and supports displaying the number of compromised hosts and security event distribution in graphs and tables. Threat case management: an alarm resource pool to store threat logs and allows users to add the logs to cases for ease of log management. |
| IPSEC | IKEv1, IKEv2 negotiation IPsec smart link selection IPsec Reverse Route Injection Peer address backup and switchback |
| EncryptionAlgorithm | ESP-DES-CBC ESP-3DES-CBC ESP-AES-128-CBC ESP-AES-192-CBC ESP-AES-256-CBC ESP-AES-128-GCM ESP-NULL SIM4-CBC MD5 SHA1 |
| Encrypted Traffic Protection | Supports HTTPS proxy and SSL encryption and decryption, and can perform content detection and filtering, auditing, and attack protection on decrypted HTTPS encrypted traffic. Support SSH encryption and decryption Support classifies and decrypt URLs to improve the protection effect |
| Virtualization | Context: virtualized logical firewalls vSystems: Lightweight virtualized independent logical devices |
| Configuration management | Remote management through Web GUI Configuration management at the CLI SNMPv3, compatible with SNMPv2 and SNMPv1 Intelligent security policy Managed by H3C SDN controller |
| Maintenance and diagnostics | Packet trace Packet capture IPsec diagnosis Dropped-Packet statistics Netstream/sflow |
| Models | LSPM6FWD, LSPM6FWDB, LSWM1FWD0, LSQM2FWDSC0, LSQM1FWDSC0, LSCM2FWDSD0, LSCM1FWDSD0, LSEM1FWESD0, IM-NGFWX-IV |
| Firewall throughput (1518 Bytes) | LSPM6FWD: 4G; LSPM6FWDB: 20G; LSWM1FWD0: 40G; LSQM2FWDSC0: 20G; LSQM1FWDSC0: 40G; LSCM2FWDSD0: 20G; LSCM1FWDSD0: 40G; LSEM1FWESD0: 60G; IM-NGFWX-IV: 60G |
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
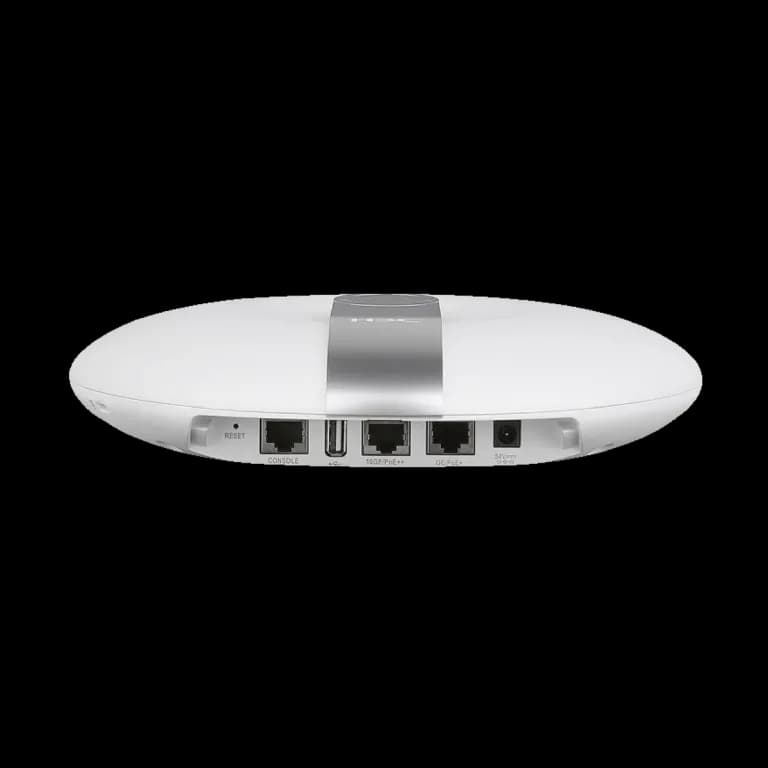
A 12-stream Wi-Fi 6 flagship with an 8x8 5 GHz radio and 10G uplink for stadiums, auditoriums and lecture halls.
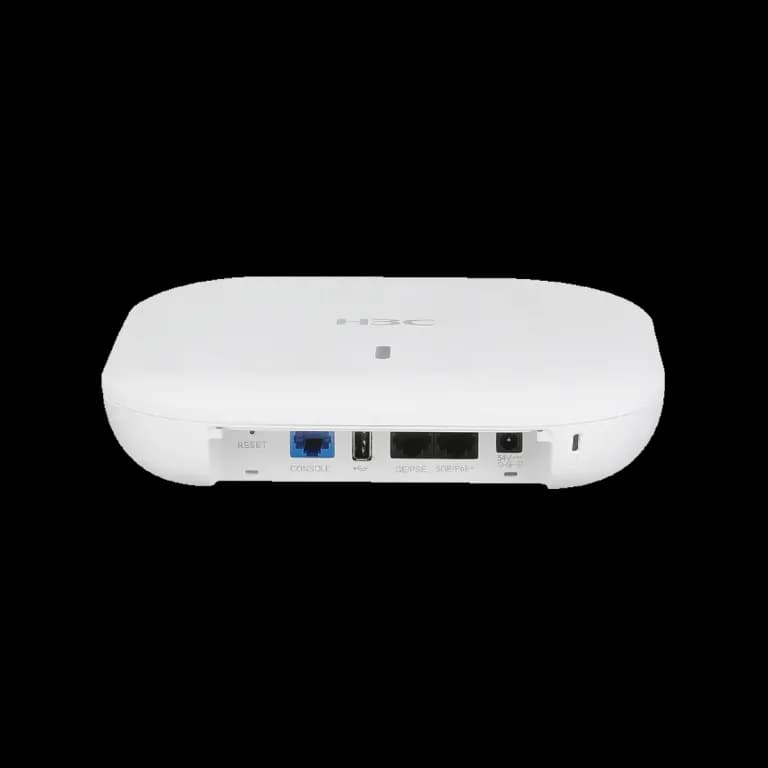
A Wi-Fi 6 AP with a 4x4 5 GHz radio and 5G multigigabit uplink for demanding indoor deployments.
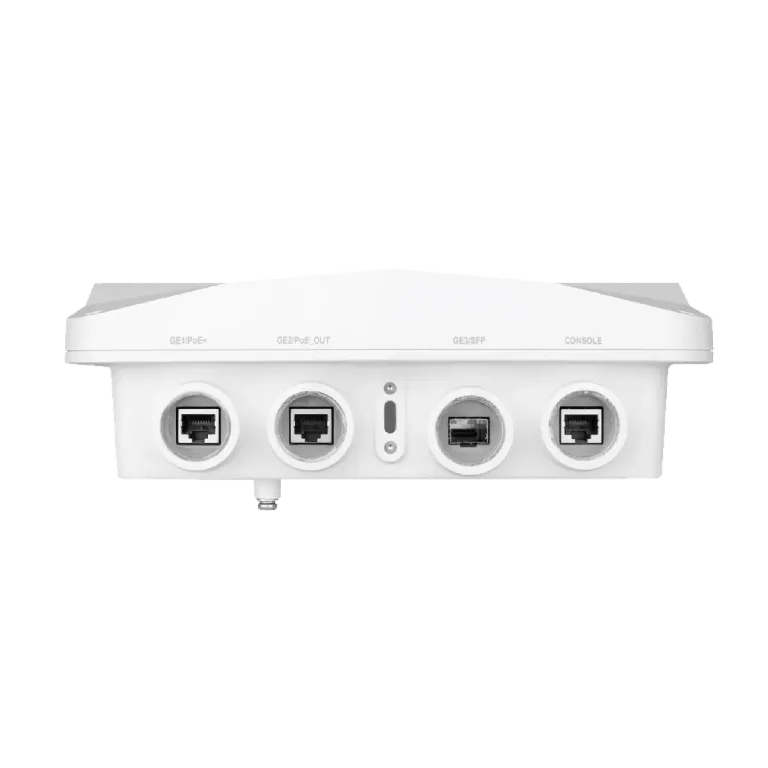
An outdoor Wi-Fi 6 AP with two 2x2 radios, switchable to dual 5 GHz, plus PoE-out for cameras or sensors.