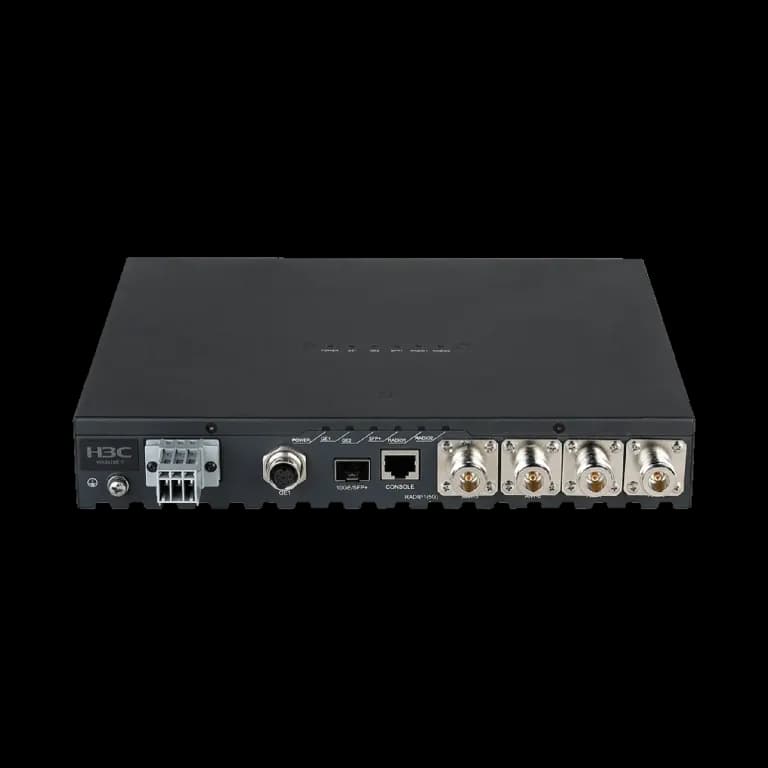
H3C WA6628E-T Wi-Fi 6 Rail Transit Access Point
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
Price on Request
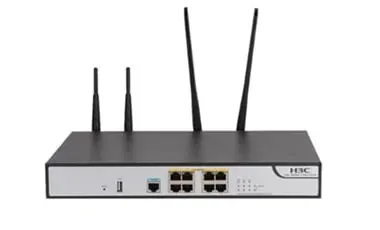
Small-office firewall/VPN gateways with built-in Wi-Fi, combining NGFW protection and wireless access.
Island-wide delivery to all 25 districts
| Models | F100-C-A3-W, F100-C-A5-W |
|---|---|
| Interface | 1x console 1x USB host 8x GE Base-T |
| WLAN | 802.11ac、802.11n |
| Dimensions (W × D × H) | 330mm*230mm*43.6mm |
| Temperature | Operating: 0°C to 45°C Storage: –30°C to +70°C |
| Humidity | Operating: 10 ~ 80%, no condensation Storage: 5 ~ 95%, no condensation |
| Operation modes | Route, transparent, and hybrid |
| Network Security | F100-C-A3-W: AAA; F100-C-A5-W: Local authentication RADIUS authentication, support PAP and CHAP authentication HWTACACS certification PKI certificate authentication AD / LDAP authentication |
| Firewall | Basic ACL and Advanced ACL Access control based on security zone Time-based access control ASPF firewall DOS / DDOS attack prevention: including SYN Flood, UDP Flood, ICMP Flood, ACK Flood, RST Flood, DNS Flood, HTTP Flood Malformed packet attacks such as: Land, Smurf, Fraggle, WinNuke, Ping of Death, Tear Drop, IP Spoofing, IP Fragmented Packet Attack, Fragmented Packet Attack, TCP Packet Illegal flag bit attack, oversized ICMP message attack, ICMP redirect or unreachable message Scanning and snooping attack prevention: port scanning, address scanning, IP routing record option message, Tracer |
| NAT | Source address NAT Support to specify the converted address pool according to policy PAT, NO-PAT Unlimited connection IP continuity, ensuring the same address after the same source conversion Easy IP Destination address NAT Point-to-point mapping of address + port Convert multiple public network addresses to the same private network address Policy-based purpose NAT Static NAT Point-to-point static NAT net-to-net static NAT NAT444 Static NAT444 Dynamic NAT444 Fullcone, solve P2P traversal problem Hairpin technology of C / S mode and P2P mode Port block incremental allocation DNS Mapping Various |
| DPI | IPS Application control and application bandwidth management Telnet, FTP, SMTP / POP3, HTTP content filtering |
| VPN | F100-C-A3-W: L2TP VPN; F100-C-A5-W: LNS Auto-Initiated LAC L2TP supports VRF |
| GRE VPN | GRE Over IPv4 GRE Over IPv6 GRE supports VRF |
| IPsec/IKE | Security protocol supports AH / ESP Support transmission and tunnel mode ESP supports three encryption algorithms: DES, 3DES and AES MD5 and SHA-1 verification algorithms Establish SA through manual or IKE Anti-replay attack IPsec policy template IPsec reverse route injection IKEV1 IKE main mode and brutal mode Support to verify IKE Peer identity through pre-shared key and certificate DPD IKE Keppalive NAT traversal VRF aware: Use IKE peer information to determine the VPN to which it belongs IPsec Dual Hot Standby IKEv2 |
| Network Protocol | F100-C-A3-W: LAN protocol; F100-C-A5-W: Ethernet_II 802.1Q |
| L2 Protocol | STP RTSP MSTP |
| IP Service | ARP Static ARP Dynamic ARP ARP proxy Free ARP DNS Local static domain name DNS Client DNS Proxy DDNS dynamic domain name service DHCP DHCP relay DHCP server DHCP client NTP NTP Client NTP Server |
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
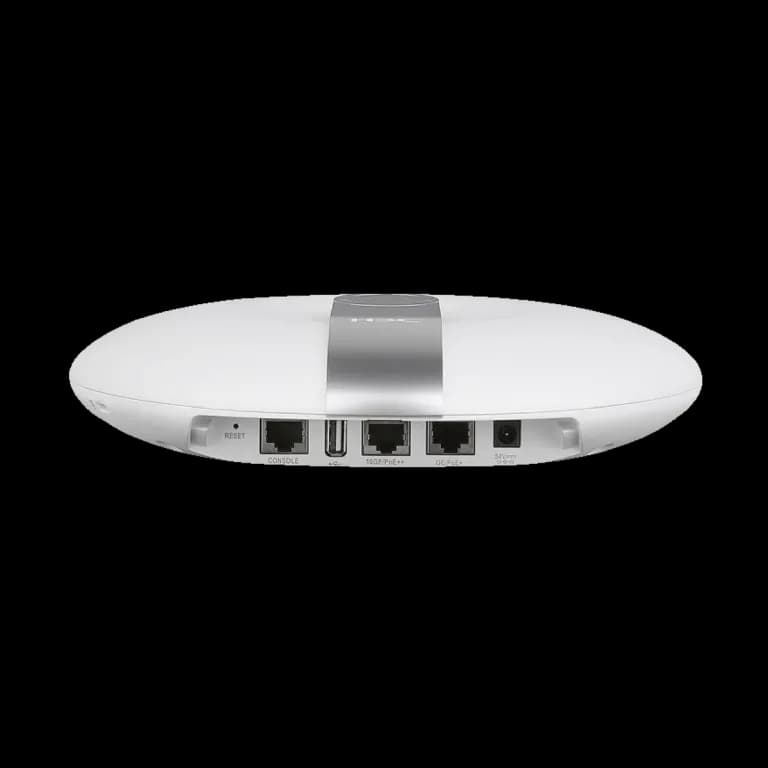
A 12-stream Wi-Fi 6 flagship with an 8x8 5 GHz radio and 10G uplink for stadiums, auditoriums and lecture halls.
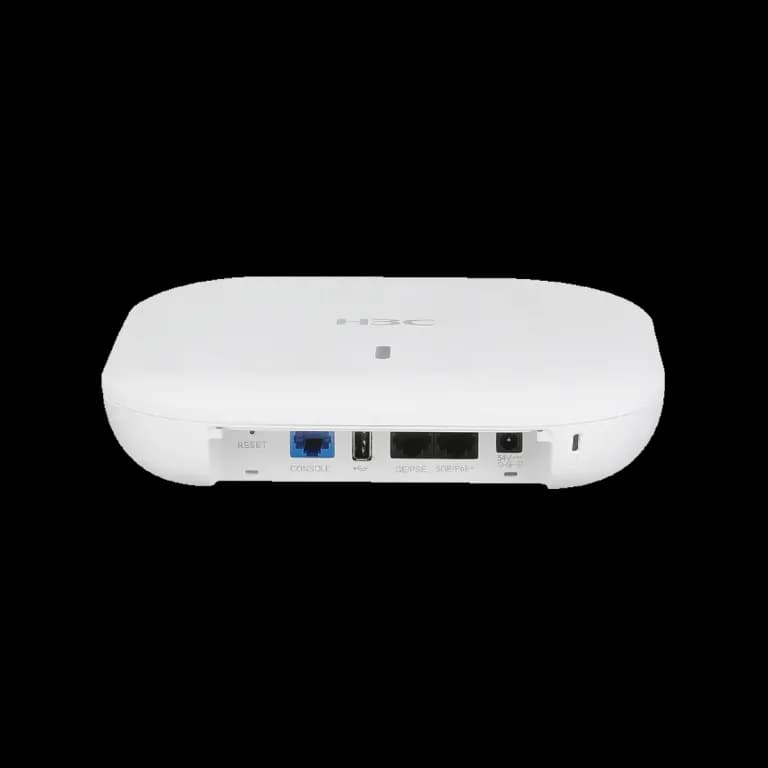
A Wi-Fi 6 AP with a 4x4 5 GHz radio and 5G multigigabit uplink for demanding indoor deployments.
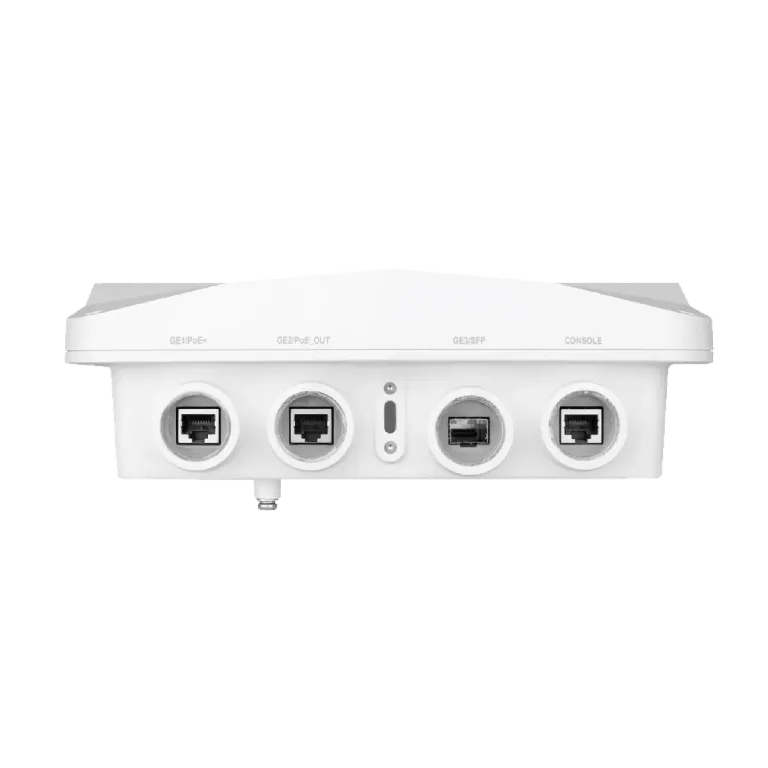
An outdoor Wi-Fi 6 AP with two 2x2 radios, switchable to dual 5 GHz, plus PoE-out for cameras or sensors.