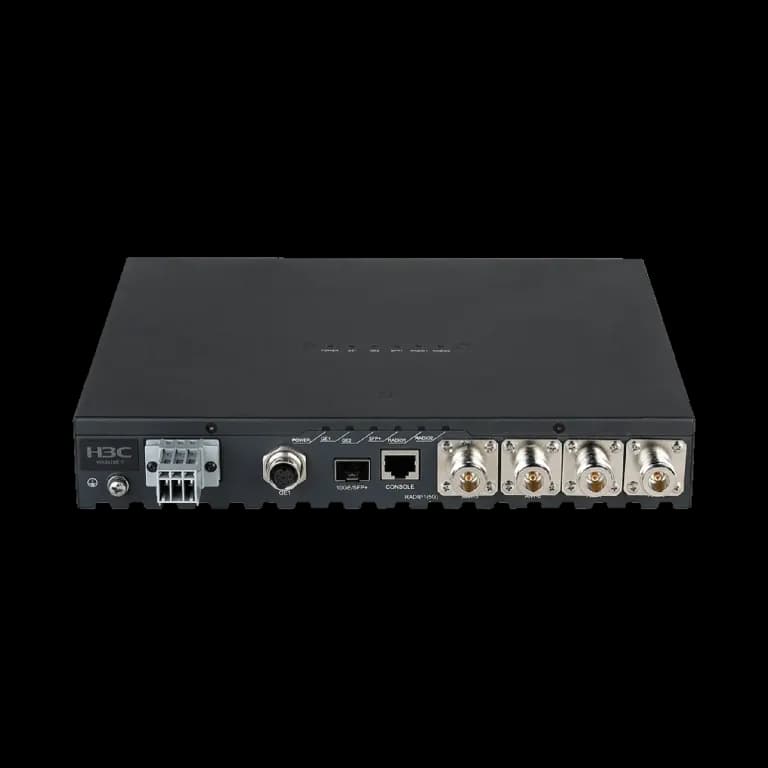
H3C WA6628E-T Wi-Fi 6 Rail Transit Access Point
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
Price on Request
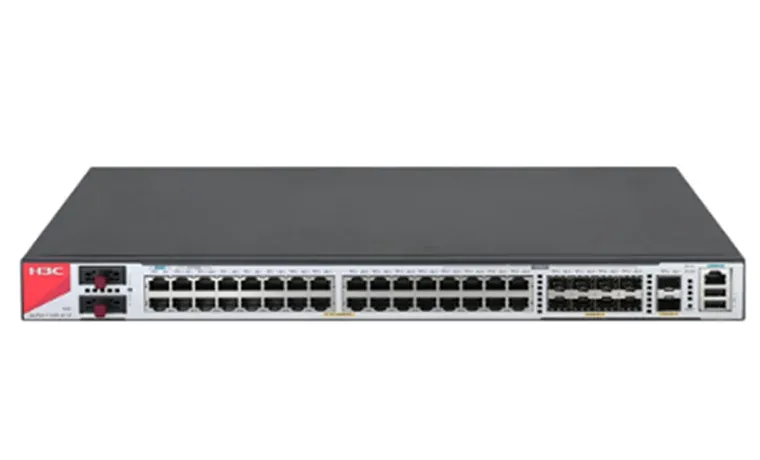
AI-enabled next-generation firewalls for branches through data centres, sharing one Comware OS and central management.
Island-wide delivery to all 25 districts
| Models | F1000-AI-05, F1000-AI-15, F1000-AI-25/35/55, F1000-AI-60/70, F1000-AI-65/75, F1000-AI-80/90 |
|---|---|
| Dimensions (W × D × H) | F1000-AI-05: 440mm×230mm×44mm; F1000-AI-15: 440mm×360mm× 44mm; F1000-AI-25/35/55: 440mm×260mm×44mm; F1000-AI-60/70: 440mm×435mm×44mm; F1000-AI-65/75: 440mm×435mm×44mm; F1000-AI-80/90: 440mm×435mm×44mm |
| USB | 2 |
| Rack mounted | Yes |
| Weight | F1000-AI-05: 3kg; F1000-AI-15: 3.7kg; F1000-AI-25/35/55: 5.4kg; F1000-AI-60/70: 10.0kg; F1000-AI-65/75: 5.6kg; F1000-AI-80/90: 10.0kg |
| Power supply | F1000-AI-05: AC; F1000-AI-15: 2*AC; F1000-AI-25/35/55: Dual hot-swappable, AC or DC; F1000-AI-60/70: Dual hot-swappable, AC or DC; F1000-AI-65/75: Dual hot-swappable, AC or DC; F1000-AI-80/90: Dual hot-swappable, AC or DC |
| Power consumption | F1000-AI-05: 32W; F1000-AI-15: 48W; F1000-AI-25/35/55: 46W; F1000-AI-60/70: 180W; F1000-AI-65/75: 90W; F1000-AI-80/90: 180W |
| MTBF(Year) | F1000-AI-05: 77.36; F1000-AI-15: 77.36; F1000-AI-25/35/55: 53.38; F1000-AI-60/70: 45.39; F1000-AI-65/75: 50.31; F1000-AI-80/90: 43.2 |
| Ports | F1000-AI-05: 1×Console Port 8×GE RJ45 Ports 2×GE Combo Ports (1 MGMT) 2×GE RJ45 Bypass Ports; F1000-AI-15: 1×Console Port 2×GE RJ45 MGMT Ports 18×GE RJ45 Ports 8×GE Combo Ports 4×GE RJ45 Bypass Ports 2×1/10GE SFP+ Ports; F1000-AI-25/35/55: 1×Console Port 1×GE RJ45 MGMT Ports 16×GE RJ45 Ports 6×GE SFP Ports 4×GE Combo Ports 2×1/10GE SFP+ Ports; F1000-AI-60/70: 1×Console Port 2×GE RJ45 MGMT Ports 14×GE RJ45 Ports 12×GE SFP Ports 4×1/10GE SFP+ Ports; F1000-AI-65/75: 1×Console Port 1×GE RJ45 MGMT Ports 16×GE RJ45 Ports 4×GE SFP Ports 4×GE Combo Ports 6×1/10GE SFP+ Ports; F1000-AI-80/90: 1×Console |
| Expansion slots | F1000-AI-05: 0; F1000-AI-15: 0; F1000-AI-25/35/55: 2; F1000-AI-60/70: 2/4; F1000-AI-65/75: 2; F1000-AI-80/90: 4 |
| Interface modules | F1000-AI-05: N/A; F1000-AI-15: N/A; F1000-AI-25/35/55: 4×GE PFC Interface Module 4×GE SFP Interface Module; F1000-AI-60/70: 4×GE PFC Interface Module 4×GE SFP Interface Module 6×1/10GE SFP+ Interface Module; F1000-AI-65/75: 4×GE PFC Interface Module 4×GE SFP Interface Module 6×1/10GE SFP+ Interface Module; F1000-AI-80/90: 4×GE PFC Interface Module 4×GE SFP Interface Module 6×1/10GE SFP+ Interface Module |
| Storage | F1000-AI-05: 480G SSD; F1000-AI-15: 480G M.2 (Raid0/Raid1); F1000-AI-25/35/55: 480G SSD; F1000-AI-60/70: 480G/1.92T SSD (Raid0/Raid1); F1000-AI-65/75: 480G/1.92T SSD (Raid0/Raid1); F1000-AI-80/90: 480G/1.92T SSD (Raid0/Raid1) |
| Flash | F1000-AI-05: 4GB; F1000-AI-15: 4GB; F1000-AI-25/35/55: 4GB; F1000-AI-60/70: 4GB; F1000-AI-65/75: 4GB; F1000-AI-80/90: 8GB |
| SDRAM | F1000-AI-05: 4GB; F1000-AI-15: 4GB; F1000-AI-25/35/55: 4GB/4GB/8GB; F1000-AI-60/70: 8GB; F1000-AI-65/75: 8GB; F1000-AI-80/90: 16GB |
| Temperature | Operating: 0°C to 45°C (32°F to 113°F) Storage: –40°C to +70°C (–40°F to +158°F) |
| Environmental protection | EU RoHS Compliance |
| EMC | FCC Part 15 (CFR 47) CLASS A ICES-003 CLASS A VCCI CLASS A CISPR 22 CLASS A EN 55022 CLASS A AS/NZS CISPR22 CLASS A CISPR 32 CLASS A EN 55032 CLASS A AS/NZS CISPR32 CLASS A CISPR 24 EN 55024 EN 61000-3-2 EN 61000-3-3 ETSI EN 300 386 GB 9254 GB 17625.1 YD/T 993 |
| Safety | UL 60950-1 CAN/CSA C22.2 No 60950-1 IEC 60950-1 EN 60950-1 AS/NZS 60950-1 FDA 21 CFR Subchapter J GB 4943.1 |
| Operation modes | Route, transparent, and hybrid |
| AAA | Portal authentication RADIUS authentication HWTACACS authentication PKI/CA (X.509 format) authentication Domain authentication CHAP authentication PAP authentication |
| Firewall | Context virtual firewall technology, which supports full virtualization of hardware resources, including CPU, memories, and storage Security zone allocation Security policy redundancy analysis Protection against malicious attacks, such as land, smurf, fraggle, ping of death, teardrop, IP spoofing, IP fragmentation, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, address/port scanning, SYN flood, ICMP flood, UDP flood, and DNS query flood Basic and advanced ACLs Time range-based ACL User-based and application-based access control ASPF application layer packet filtering St |
| Antivirus | Signature-based virus detection Manual and automatic upgrade for the signature database Stream-based processing Virus detection based on HTTP, FTP, SMTP, and POP3 Virus types include Backdoor, Email-Worm, IM-Worm, P2P-Worm, Trojan, AdWare, and Virus Virus logs and reports |
| Deep intrusion prevention | Prevention against common attacks such as hacker, worm/virus, Trojan, malicious code, spyware/adware, DoS/DDoS, buffer overflow, SQL injection, and IDS/IPS bypass Attack signature categories (based on attack types and target systems) and severity levels (including high, medium, low, and notification) Manual and automatic upgrade for the attack signature database (TFTP and HTTP). P2P/IM traffic identification and control Detection of the real source IP address of HTTP packet Source tracing and alarming base on attack event: log, email alert, collect hit statistics, packet capture, upload packet |
| Email/webpage/application layer filtering | Email filtering SMTP email address filtering Email subject/content/attachment filtering Flow-basedwebfiltering HTTP URL/content filtering Java blocking ActiveX blocking HTTPS traffic filtering: SNI extraction based on SSL negotiation process SQL injection attack prevention |
| Asset-security analysis | Botnet Analysis: analyses all security logs related to botnets and supports displaying information about hosts that might be zombie hosts, including zombie host IP and peer IP Security Analysis: analyzes health status of hosts and supports displaying the number of compromised hosts and security event distribution in graphs and tables. Threat case management: an alarm resource pool to store threat logs and allows users to add the logs to cases for ease of log management. |
| NAT | Many-to-one NAT, which maps multiple internal addresses to one public address Many-to-many NAT, which maps multiple internal addresses to multiple public addresses One-to-one NAT, which maps one internal address to one public address NAT of both source address and destination address External hosts access to internal servers Internal address to public interface address mapping NAT support for DNS Setting effective period for NAT NAT ALGs for NAT ALG, including DNS, FTP, H.323, ILS, MSN, NBT, PPTP, and SIP NAT64 Policy, NAT translation between IPv4 networks and IPv6 networks. NAT66 Policy, NAT |
| VPN | L2TP VPN IPSec VPN GRE VPN SSL VPN VPN Client on Windows, Android, iOS, macOS, Ubuntu ADVPN |
| IPSEC | IKEv1, IKEv2 negotiation IPsec smart link selection IPsec Reverse Route Injection Peer address backup and switchback |
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
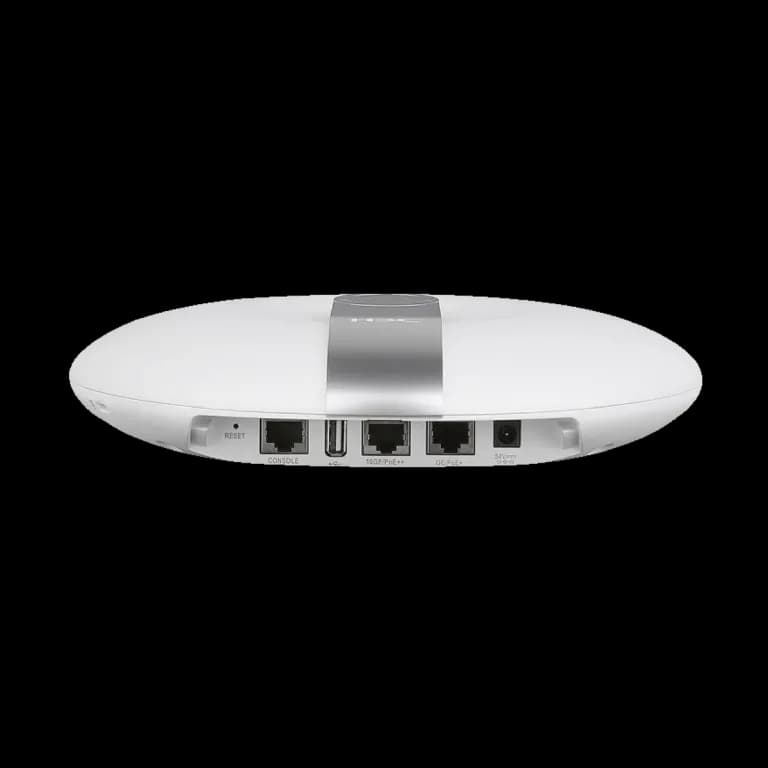
A 12-stream Wi-Fi 6 flagship with an 8x8 5 GHz radio and 10G uplink for stadiums, auditoriums and lecture halls.
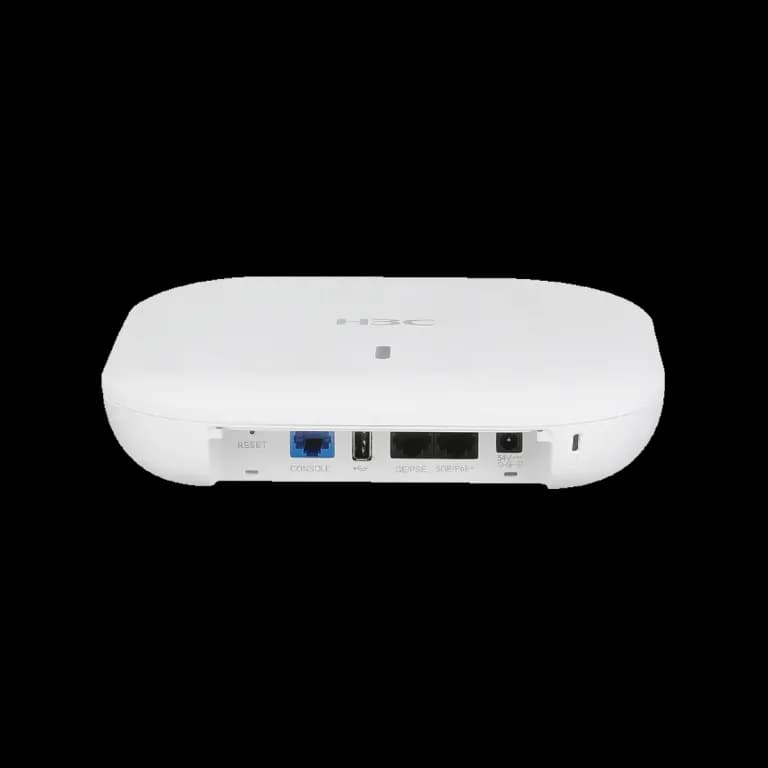
A Wi-Fi 6 AP with a 4x4 5 GHz radio and 5G multigigabit uplink for demanding indoor deployments.
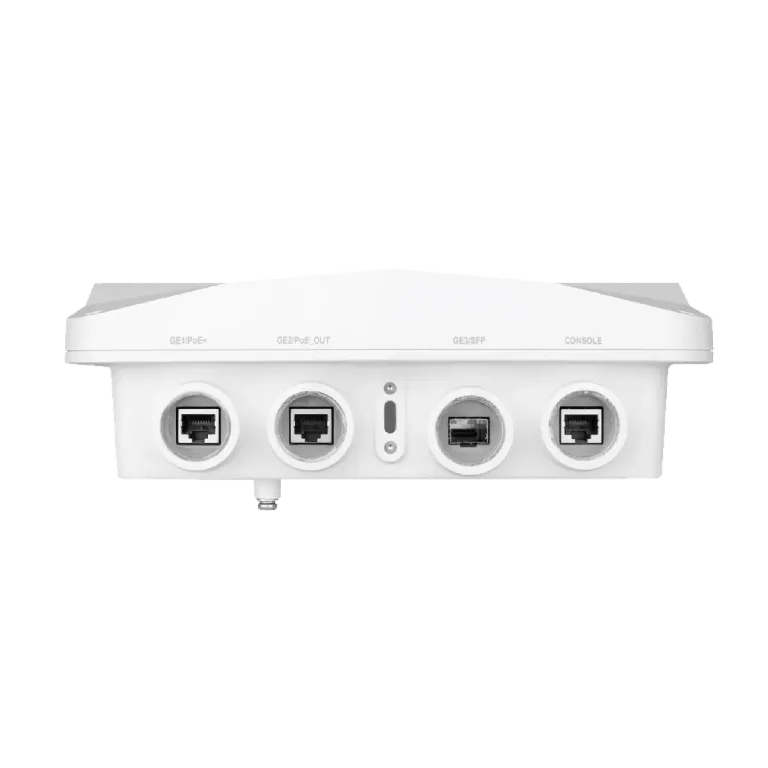
An outdoor Wi-Fi 6 AP with two 2x2 radios, switchable to dual 5 GHz, plus PoE-out for cameras or sensors.