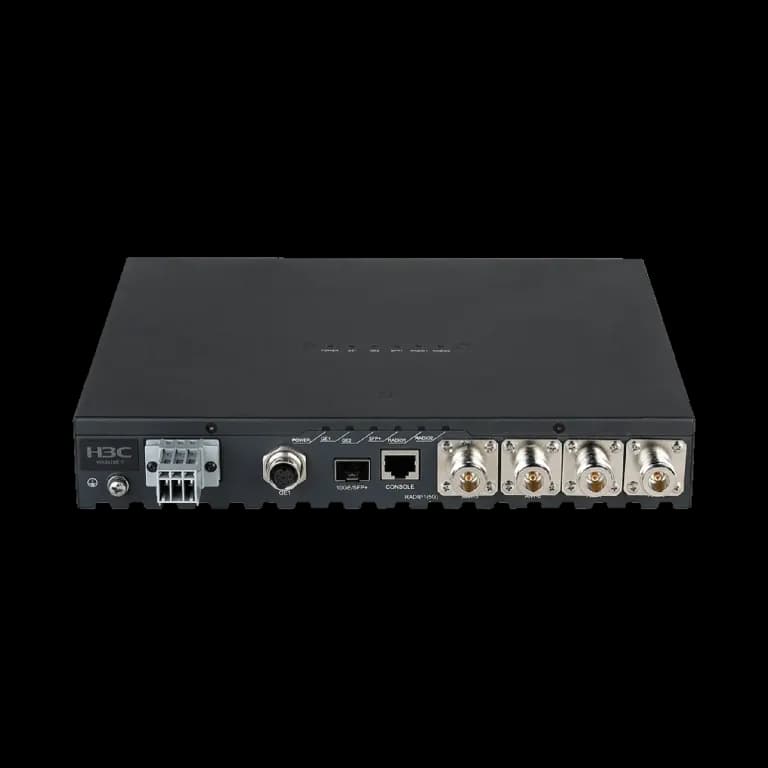
H3C WA6628E-T Wi-Fi 6 Rail Transit Access Point
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
Price on Request
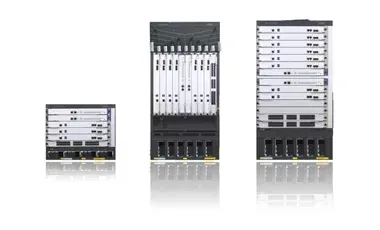
ICSA-certified chassis security gateways for cloud data centres, carrier CGN and large enterprises.
Island-wide delivery to all 25 districts
| Models | M9006, M9010, M9014 |
|---|---|
| MPU slots | 2 |
| LPU slots | M9006: 4; M9010: 8 (vertical); M9014: 12 |
| Switching fabric module slots | 4 |
| Redundancy design | Redundant MPUs, switching fabric modules, power modules, and fan trays |
| Size (W X H X D) | M9006: 440mm x 353mm x 660 mm(8RU); M9010: 440mm x 886mm x 660mm(20RU); M9014: 440mm x 797mm x 660mm (18RU) |
| Weight(Kg) | M9006: < 85kg; M9010: < 143kg; M9014: < 145kg |
| Power(W) | M9006: <1331W; M9010: <2252W; M9014: <3360W |
| Throughputs (*With two I/O modules) | M9006: 160G; M9010: 480G; M9014: 800G |
| Maximum Concurrent connections per single firewall blade | 40M |
| Connections per second per single firewall blade | 600K/S |
| IPSEC Throughputs (3DES,1400bytes) per single firewall blade | 20G |
| IPSEC concurrent tunnel per single firewall blade | 50K |
| Ambient temperature | Operating: 0°C to 45°C (32°F to 113°F) Non operating: –40°C to +70°C (–40°F to +158°F) |
| Operating mode | Route |
| AAA | Portal authentication RADIUS authentication HWTACACS authentication PKI/CA (X.509 format) authentication Domain authentication CHAP authentication PAP authentication |
| Multi-service security gateway | Virtual multi-service security gateway Security zone Attack protection against malicious attacks, such as land, smurf, fraggle, ping of death, tear drop, IP spoofing, IP fragmentation, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, address/port scanning, SYN flood, ICMP flood, UDP flood, and DNS query flood Basic and advanced ACL Time range-based ACL Dynamic packet filtering ASPF application layer packet filtering Static and dynamic blacklist function MAC-IP binding MAC-based ACL 802.1Q VLAN transparent transmission |
| NAT | Many-to-one NAT, which maps multiple internal addresses to one public address Many-to-many NAT, which maps multiple internal addresses to multiple public addresses One-to-one NAT, which maps one internal address to one public address NAT of both source address and destination address External hosts access to internal servers Internal address to public interface address mapping NAT support for DNS Setting effective period for NAT NAT ALGs for NAT ALG, including DNS, FTP, H.323, ILS, MSN, NBT, PPTP, and SIP |
| VPN | L2TP VPN IPSec VPN GRE VPN SSL VPN |
| IPv6 | IPv6 status firewall IPv6 interzone policy IPv6 attack protection IPv6 connection limit IPv6 protocols such as ICMPv6, PMTU, Ping6, DNS6, TraceRT6, Telnet6, DHCPv6 Client, and DHCPv6 Relay. IPv6 routing: RIPng, OSPFv3, BGP4+, static routing, policy-based routing, PIM-SM, and PIM-DM IPv6 transition techniques: NAT-PT, IPv6 tunneling, NAT64 (DNS64), and DS-LITE |
| High availability | Active/active and active/standby stateful failover IFF SCF Asymmetric-path mode stateful failover IKE-based IPsec VRRP Static and dynamic link aggregation BFD ISSU Patch images |
| Configuration management | Configuration management at the CLI Remote management through Web Device management through H3C IMC SNMPv3, compatible with SNMPv2c and SNMPv1 |
| Environmental protection | RoHS |
| Certifications | ICSA Labs |
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
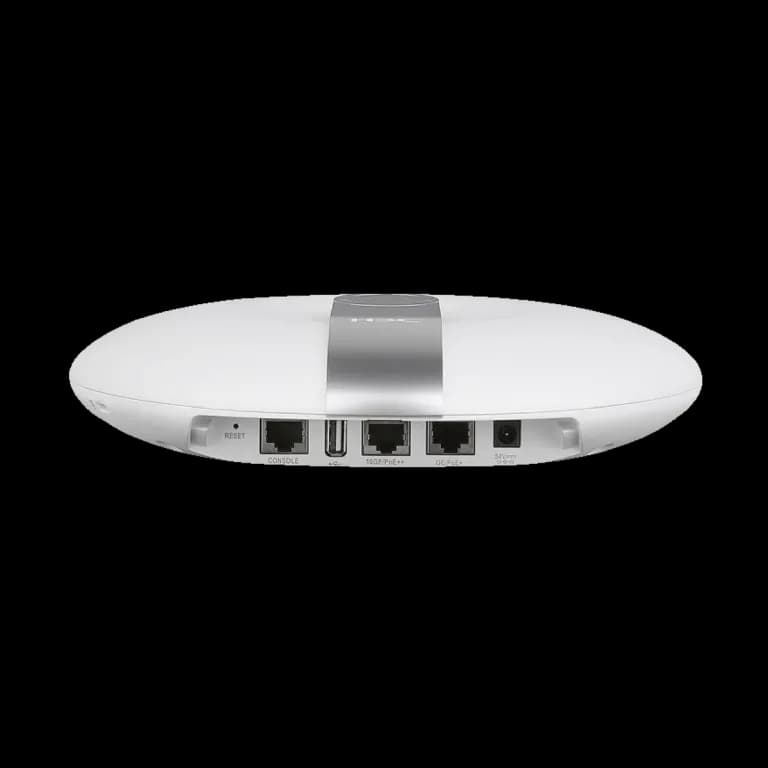
A 12-stream Wi-Fi 6 flagship with an 8x8 5 GHz radio and 10G uplink for stadiums, auditoriums and lecture halls.
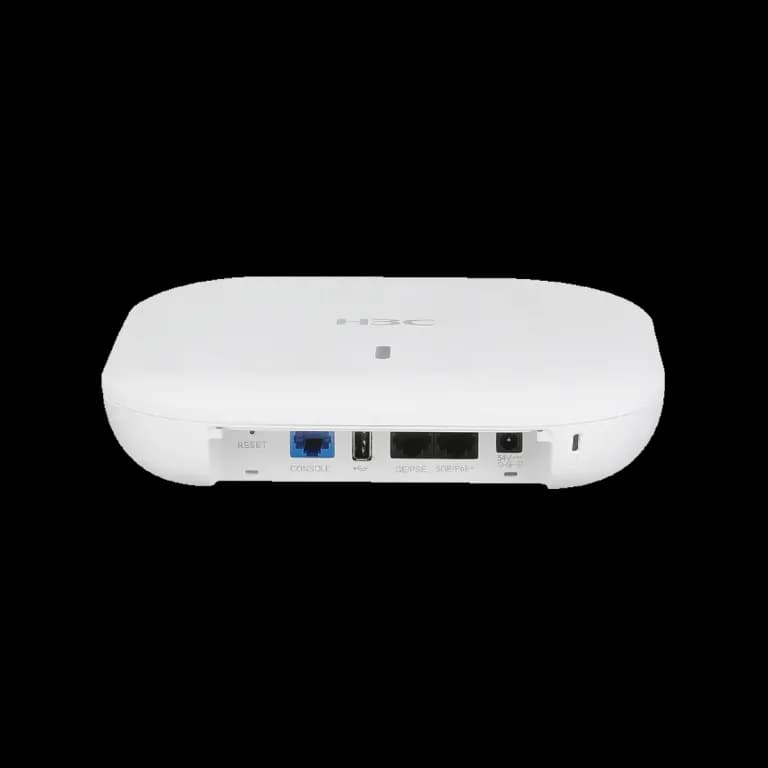
A Wi-Fi 6 AP with a 4x4 5 GHz radio and 5G multigigabit uplink for demanding indoor deployments.
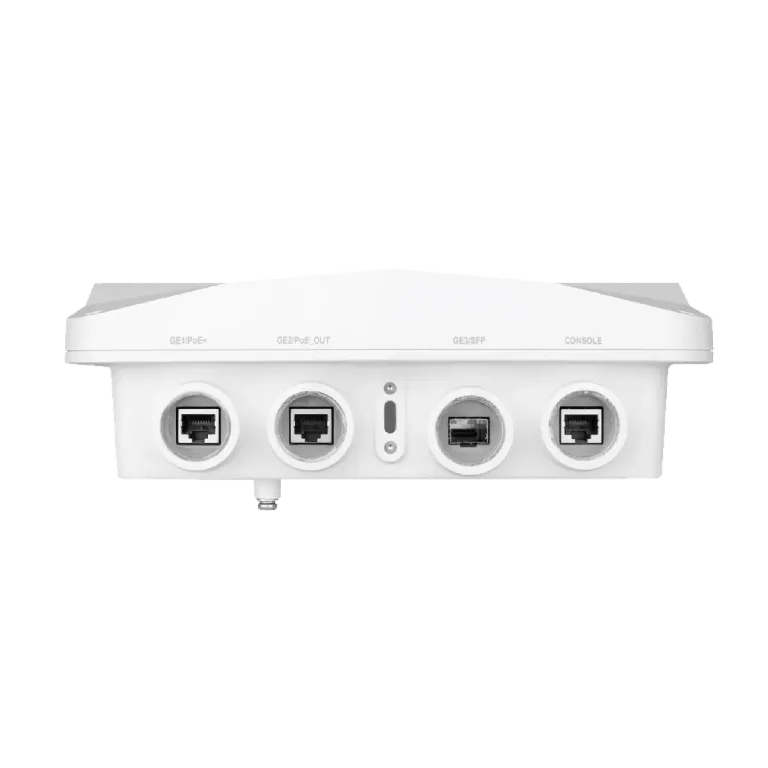
An outdoor Wi-Fi 6 AP with two 2x2 radios, switchable to dual 5 GHz, plus PoE-out for cameras or sensors.