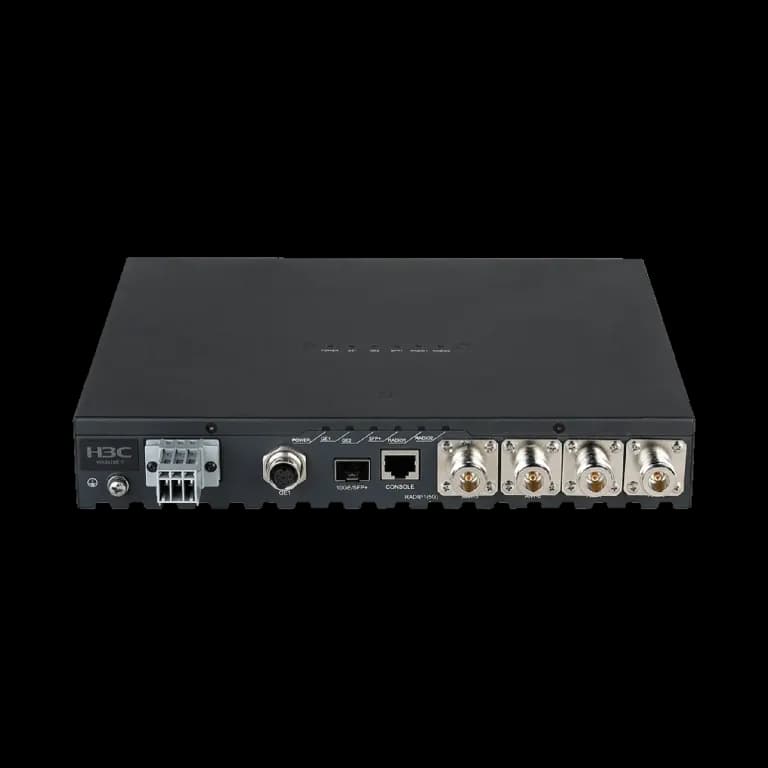
H3C WA6628E-T Wi-Fi 6 Rail Transit Access Point
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
Price on Request
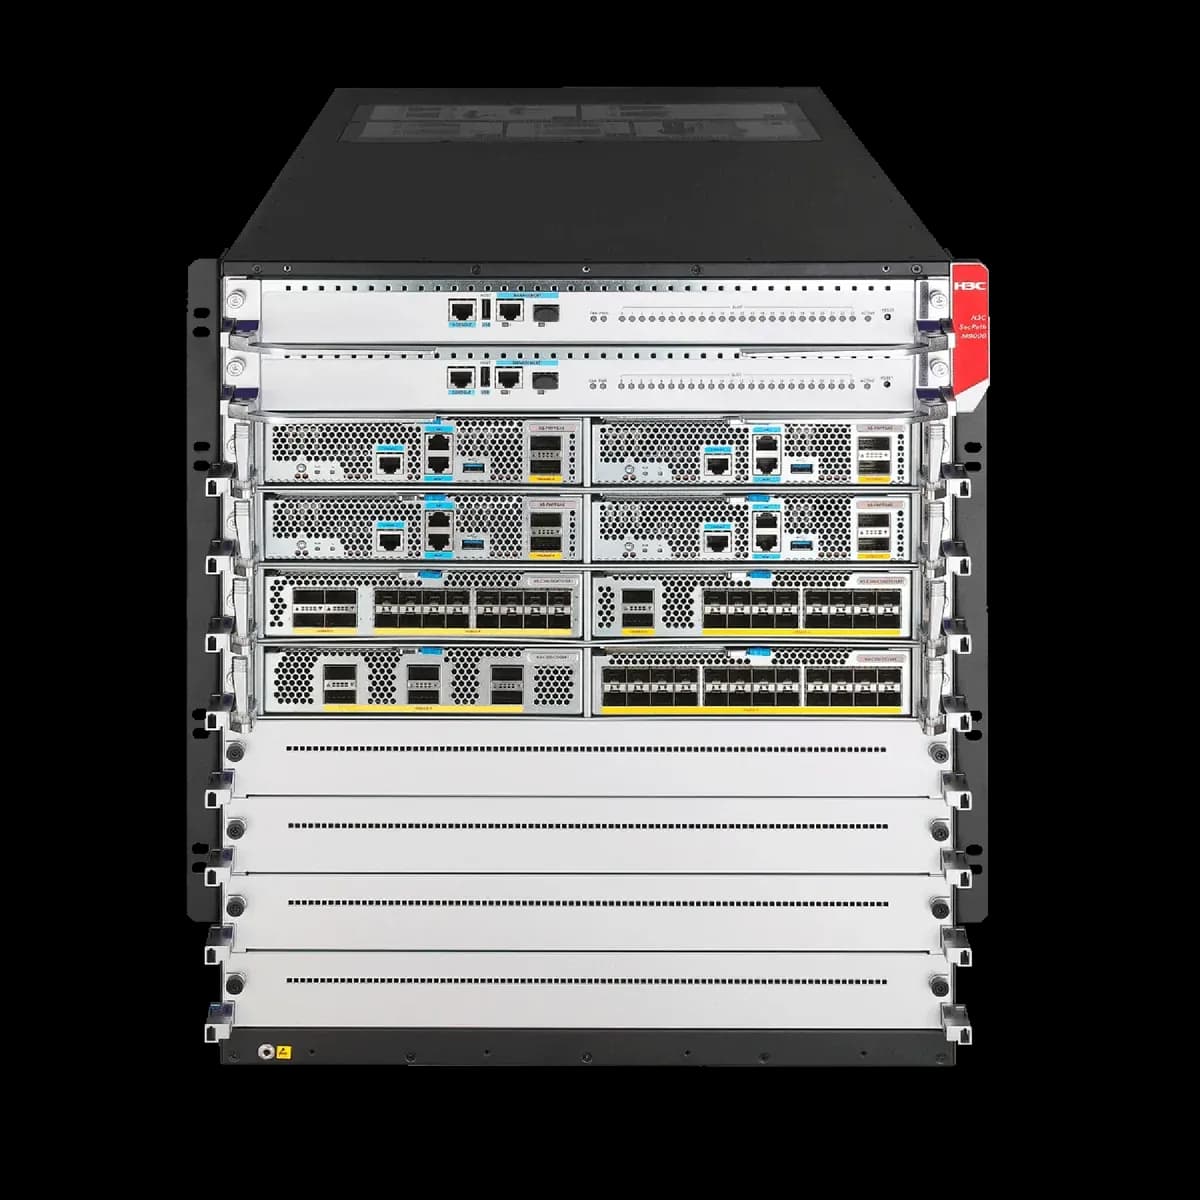
H3C's highest-throughput chassis firewall for carrier cores, large enterprises and campus internet edges, built on a fully distributed architecture.
Island-wide delivery to all 25 districts
| Models | M9000-X06, M9000-X10 |
|---|---|
| Number of main control board slots | 2 |
| Number of service board slots | M9000-X06: 8; M9000-X10: 16 |
| Number of SFU slots | 4 |
| Redundant design | Main control, SFU, power supply, fan |
| Dimensions ( W x H x D) | M9000-X06: 440mm×264mm×857mm (6RU); M9000-X10: 440mm×530mm×857mm ( 12 RU) |
| Weight ( Kg) | M9000-X06: < 120 Kg; M9000-X10: < 220 Kg |
| Total power consumption (W) | M9000-X06: <2252W; M9000-X10: <3360W |
| Ambient temperature | 0 ~40°C Non-working: -40~70°C |
| Environmental protection | EU RoHS Compliance |
| EMC | FCC Part 15 (CFR 47) CLASS A ICES-003 CLASS A VCCI CLASS A CISPR 22 CLASS A EN 55022 CLASS A AS/NZS CISPR22 CLASS A CISPR 32 CLASS A EN 55032 CLASS A AS/NZS CISPR32 CLASS A CISPR 24 EN 55024 EN 61000-3-2 EN 61000-3-3 ETSI EN 300 386 GB 9254 GB 17625.1 YD/T 993 |
| Safety | UL 60950-1 CAN/CSA C22.2 No 60950-1 IEC 60950-1 EN 60950-1 AS/NZS 60950-1 FDA 21 CFR Subchapter J GB 4943.1 |
| Environmental protection and certification | Support Europe's strict RoHS environmental protection certification |
| Operating mode | Routing mode, transparent mode, bridge mode |
| AAA service | Portal authentication, RADIUS authentication, HWTACACS authentication, PKI/CA (X.509 format) authentication, domain authentication Support manual key, IKEv2, redundant VPN gateway, EAP authentication, IKEv2 redirection |
| Firewall | Virtual firewall Security area division Can defend against Land, Smurf, Fraggle, Ping of Death, Tear Drop, IP Spoofing, IP Fragmentation, ARP spoofing, ARP active reverse query, TCP message flag bit illegal oversized ICMP message, address scanning, port scanning, SYN Flood, UPD Flood, ICMP Flood, DNS Flood and other malicious attacks Dynamic packet filtering, ASPF application layer packet filtering Static and dynamic blacklist functions MAC and IP binding function MAC-based access control list ICMPv6, DHCPv6 Support 802.1q VLAN transparent transmission MLD, ND |
| Security strategy | Access control lists based on domain name (domain name group), service, user, application, time period, etc. Supports strategic risk classification and application risk tuning Policies can be fuzzily queried to retrieve redundant and no-hit policies Supports policy grouping, and can be connected to third-party platforms through the NETCONF interface to create, delete, modify, and move policies Security monitoring based on state legitimacy Support access control based on black and white lists, and support one-click setting of black and white lists based on alarms |
| Routing function | Support static routing Support dynamic routing: RIP, OSPF, BGP, ISIS and other routing protocols Support policy routing based on source/destination IP, source/destination port, service, application type, user and user group, outbound/incoming interface, link state, etc. |
| Virus detection | Supports virus feature detection and protection based on IPV4 and IPv6 dual stacks, and can detect email viruses, web application viruses, common file viruses, Trojan horses, worms, malicious web pages, compressed data, packers and compressed packages (zip, gzip, tar) virus killing Support manual and automatic upgrade of virus database, support manual import of signature database Support cloud virus database Packet Flow Processing Mode Support HTTP, FTP, SMTP, POP3 protocol Supported virus types: Backdoor, Email-Worm, IM-Worm, P2P-Worm, Trojan, AD-Ware, Virus, etc. Support virus logs and repor |
| Web security protection | Support web security detection Support CC attack protection Supports server abnormal outreach detection, and can customize learning parameters Support web page hanging horse, Trojan horse, and other attack protection password and password brute force cracking detection and protection for common web services ( including HTTP, FTP, SSH, SMTP, IMAP, etc.), common database software (MySQL, Oracle, MSSQL) |
| Deep security | Supports defense against hacker attacks, worms/viruses, Trojan horses, malicious codes, spyware/adware, etc., can subdivide strategies and formulate intrusion defense templates according to different scenarios Supports Flood attacks at the application layer (HTTP, HTTPS, DNS, FTP, SIP, etc.), can set the learning time and threshold through machine self-learning, and automatically generate DDoS prevention strategies based on the results Support buffer overflow, SQL injection, IDS/IPS escape and other attack defense Support the classification of attack signature database (classification accordin |
| Encrypted traffic protection | Supports HTTPS proxy and SSL encryption and decryption, and can perform content detection and filtering, auditing, and attack protection on decrypted HTTPS encrypted traffic. Support SSH encryption and decryption Support classify and decrypt URLs to improve the protection effect |
| Mail / Web/Application layer filtering | Email filtering SMTP email address filtering Email header filtering Email Content Filtering Email attachment filtering Web filtering HTTP URL filtering HTTP content filtering Application Layer Filtering Java Blocking ActiveX Blocking Defense against SQL injection attacks |
| Smart bandwidth control | Supports bandwidth guarantee based on user, IP, interface, and service, supports traffic shaping, and supports maximum/minimum flow and connection speed limit management for each IP and user It can support setting flow control policies based on application layer protocols, and can set maximum/minimum bandwidth, guaranteed bandwidth, protocol traffic priority, etc., and supports eight-level control |
| Load balancing | Support application layer link load balancing based on HTTP and HTTPS Support DNS transparent proxy, support DNS filtering, support intelligent DNS Support server load balancing Support global load Support link health status detection Support intelligent link selection |
| Nat | Support multiple internal addresses mapped to the same public network address Support mapping of multiple internal addresses to multiple public network addresses Support one-to-one mapping from internal addresses to public network addresses Support port multiplexing technology, which can increase the upper limit of NAT conversion Supports simultaneous translation of source and destination addresses, real-time alarm when the usage of the source NAT address pool exceeds the limit Support external network hosts to access internal servers Support direct mapping of internal addresses to interface p |
| VPN | L2TP VPN, IPSec VPN, GRE VPN, MPLS VPN, SSL VPN Support IPv6 over IPv4 GRE tunnel |
| EncryptionAlgorithm | ESP-DES-CBC ESP-3DES-CBC ESP-AES-128-CBC ESP-AES-192-CBC ESP-AES-256-CBC ESP-AES-128-GCM ESP-NULL SM1-CBC-128 SIM4-CBC MD5 SHA1 SM3 |
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
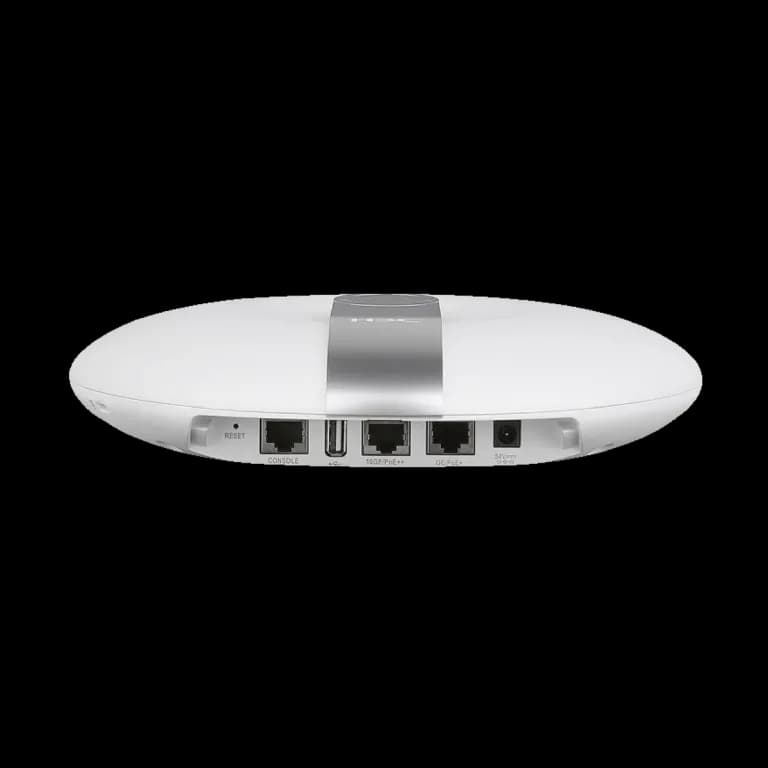
A 12-stream Wi-Fi 6 flagship with an 8x8 5 GHz radio and 10G uplink for stadiums, auditoriums and lecture halls.
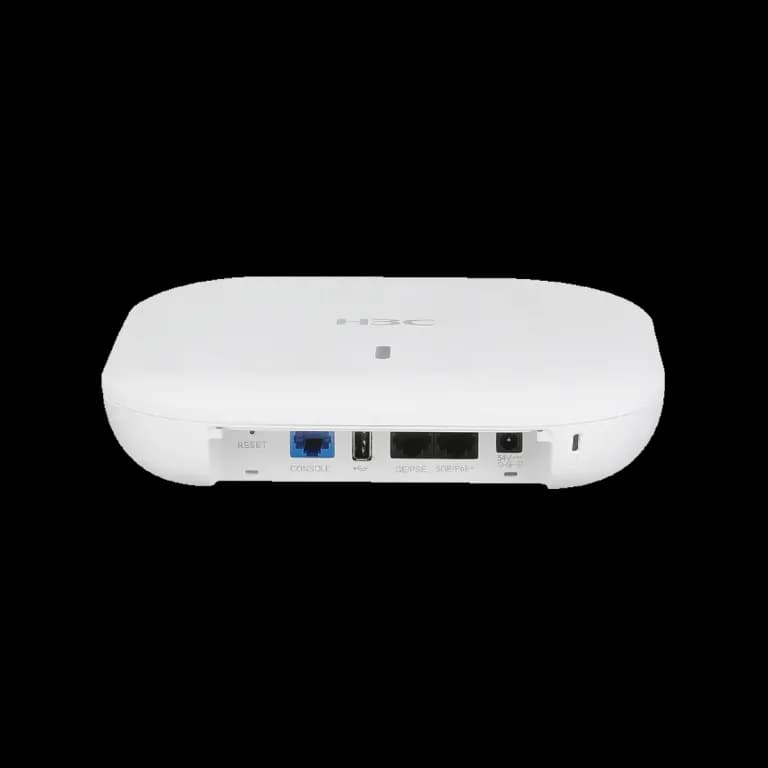
A Wi-Fi 6 AP with a 4x4 5 GHz radio and 5G multigigabit uplink for demanding indoor deployments.
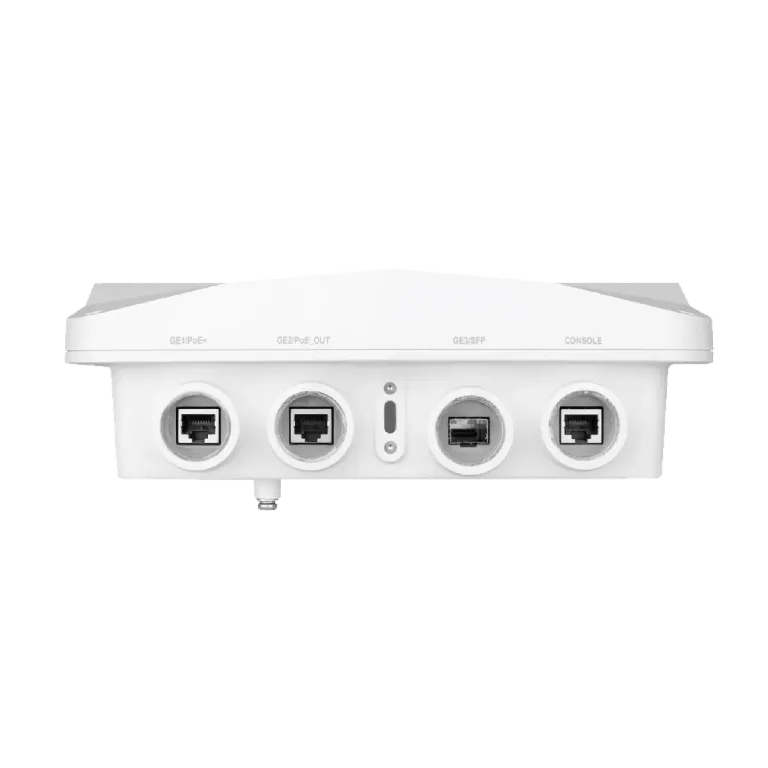
An outdoor Wi-Fi 6 AP with two 2x2 radios, switchable to dual 5 GHz, plus PoE-out for cameras or sensors.