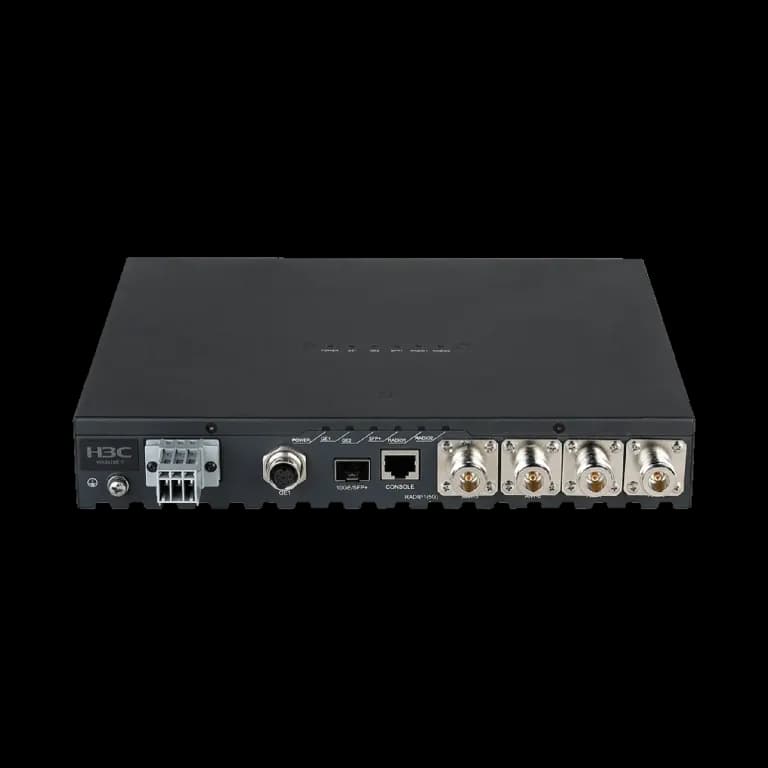
H3C WA6628E-T Wi-Fi 6 Rail Transit Access Point
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
Price on Request
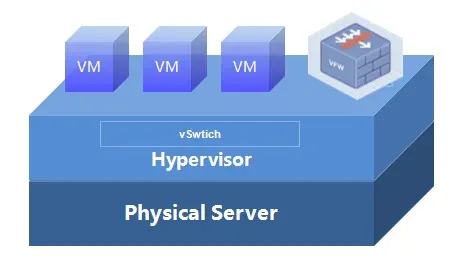
A software firewall for VMware, KVM and H3C CAS that protects virtualised data centres and clouds.
Island-wide delivery to all 25 districts
| Software image | H3C SecPath vFW1000 software image in ISO, OVA, QCOW2, or IPE format |
|---|---|
| Hypervisor | VMware ESXi Linux KVM H3C CAS |
| VM resources | A minimum of 1 vCPU (above 2.0 GHz clock speed ) A minimum of 1 GB memory A minimum of 8 GB drive 2 to 16 vNICs, vNIC types: E1000, VMXNET3, VirtIO, and Intel 82599VF |
| Ethernet | Layer 3 Ethernet interface/subinterface, Layer 2 Ethernet interface ARP 802.1Q VLAN, VLAN termination PPPoE client |
| IP routing | Static routing Dynamic routing: RIPv1/v2, OSPFv2, BGP Routing policy |
| IP services | Forwarding/fast forwarding TCP, UDP, IP Option, IP unnumbered PBR Ping, tracert DHCP server, DHCP relay, DHCP client DNS client, DNS proxy, DDNS FTP server, FTP client, TFTP client Telnet server, Telnet client NTPv3/NTPv4/SNTPv3/SNTPv4 AFT SSHv1.5/2.0, SSL |
| IPv6 | IPv6 ND, IPv6 PMTU, IPv6 FIB, IPv6 ACL IPv6 over IPv4 manual tunneling, automatic IPv4-compatible IPv6 tunneling, 6to4 tunneling, ISATAP tunneling Static routing Dynamic routing: RIPng, OSPFv3, BGP4+ IPv6 packet filtering IPv6 ASPF IPv6 interzone policy IPv6 attack defense |
| AAA | Portal authentication RADIUS authentication HWTACACS authentication PKI/CA (X509 format) authentication Domain authentication CHAP authentication PAP authentication |
| Firewall | Security zone, packets from a different security zone denied by default Defending against various malicious attacks, including land, smurf, fraggle, ping of death, teardrop, IP spoofing, IP fragmentation, ARP spoofing, reverse ARP lookup, invalid TCP flag, large ICMP packet, address/port scanning, SYN flood, ICMP flood, and UDP flood Basic and advanced ACLs Interface-based ACLs Time range-based ACLs Dynamic packet filtering ASPF application layer packet filtering Static and dynamic blacklist MAC-IP binding MAC-based ACL Connection limit FIPS/CC mode |
| NAT | Many-to-one NAT, which maps multiple internal addresses to one public address Many-to-many NAT, which maps multiple internal addresses to multiple public addresses One-to-one NAT, which maps one internal address to one public address NAT of both source address and destination address External hosts access to internal servers Internal address to public interface address mapping NAT support for DNS Setting effective period for NAT NAT ALGs for NAT ALG, including DNS, FTP, TFTP, PPTP, H.323, SIP, RSH, ILS, MSN, NBT |
| VPN | L2TP VPN / Initiating a tunneling request to the LNS with the complete VPN username and the ISP domain name to which the user belongs. IP assignment to VPN users CHAP authentication to reauthenticate users and LCP renegotiation |
| IPsec/IKE | AH, ESP Setting up a security association automatically through IKE or manually Multiple ESP encryption algorithms including DES, 3DES, and AES MD5 and SHA-1 authentication algorithms IKE main-mode and aggressive-mode NAT traversal DPD |
| GRE VPN | - |
| QoS | Traffic classification based on port, MAC address, IP address, IP priority, DSCP priority, TCP/UDP port number, or protocol type Congestion management: FIFO, WFQ, CBQ Congestion avoidance: Tail drop, WRED |
| DC | VXLAN, OpenFlow1.3 |
| High availability | VRRP/VRRPv3 BFD Reth IRF |
| Management and maintenance | User access management: console port, AUX port, SSH, Telnet, FTP Local management: CLI, automatic configuration, file system Network management: SNMPv1/v2c/v3, IMC, MIB, TR069, H3C IMC security management center, NETCONF Network monitoring: SNMPv1/v2c/v3, RMON, Syslog, NQA, sFlow, track, NetStream, EAA Others: Tcl, Python |
| Models | 1 × vCPU & 2G memory, 4 × vCPUs & 8G memory, 8 × vCPUs & 16G memory |
| FW throughput | 1 × vCPU & 2G memory: 9Gbps; 4 × vCPUs & 8G memory: 37Gbps; 8 × vCPUs & 16G memory: 45Gbps |
| Threat protection | 1 × vCPU & 2G memory: 1.6Gbps; 4 × vCPUs & 8G memory: 7Gbps; 8 × vCPUs & 16G memory: 16Gbps |
| IPSec VPN throughput | 1 × vCPU & 2G memory: 960Mbps; 4 × vCPUs & 8G memory: 1.9Gbps; 8 × vCPUs & 16G memory: 5Gbps |
| Concurrent sessions | 1 × vCPU & 2G memory: 1.2 million; 4 × vCPUs & 8G memory: 8 million; 8 × vCPUs & 16G memory: 14 million |
| Threat protection throughput(APP+IPS+AV+URL) | 1 × vCPU & 2G memory: 800Mbps; 4 × vCPUs & 8G memory: 1.2Gbps; 8 × vCPUs & 16G memory: 2.5Gbps |
| Models | 1 × vCPU & 2G memory, 4 × vCPUs & 8G memory, 8 × vCPUs & 16G memory |
| New sessions per second | 1 × vCPU & 2G memory: 20 thousand; 4 × vCPUs & 8G memory: 60 thousand; 8 × vCPUs & 16G memory: 120 thousand |
An all-metal Wi-Fi 6 AP for trains and vehicles, with M12 connectors and resistance to strong electromagnetic interference.
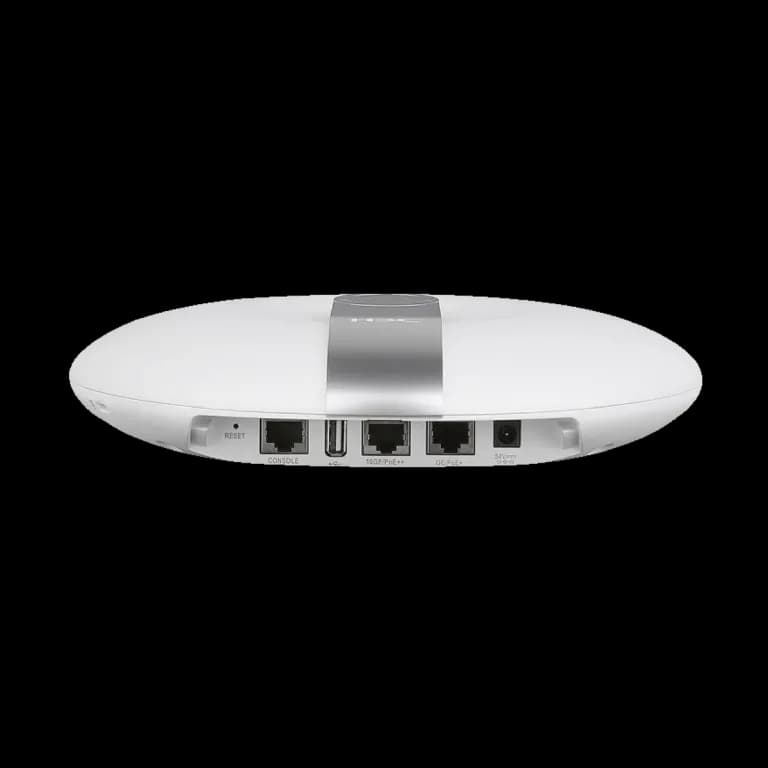
A 12-stream Wi-Fi 6 flagship with an 8x8 5 GHz radio and 10G uplink for stadiums, auditoriums and lecture halls.
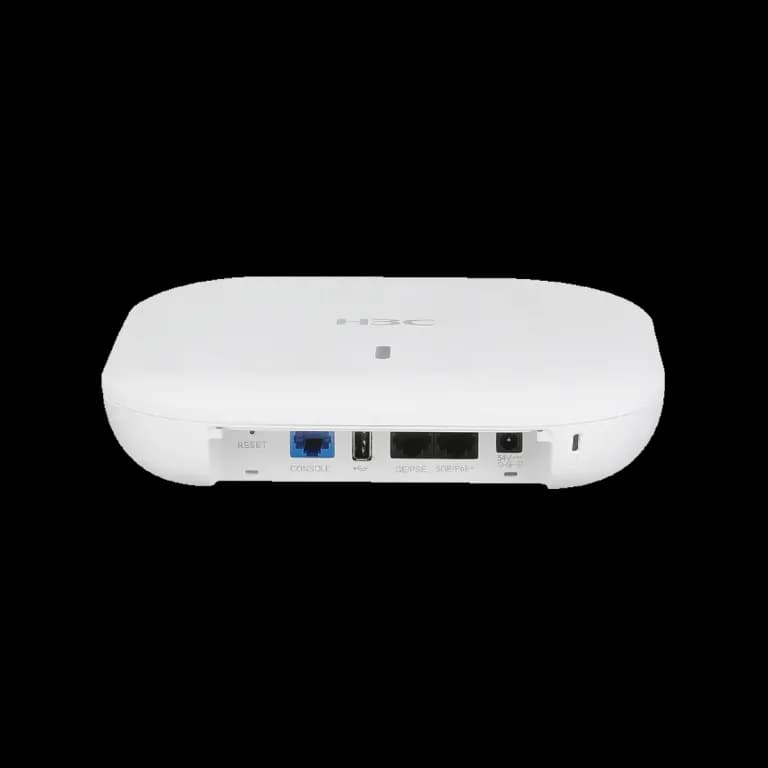
A Wi-Fi 6 AP with a 4x4 5 GHz radio and 5G multigigabit uplink for demanding indoor deployments.
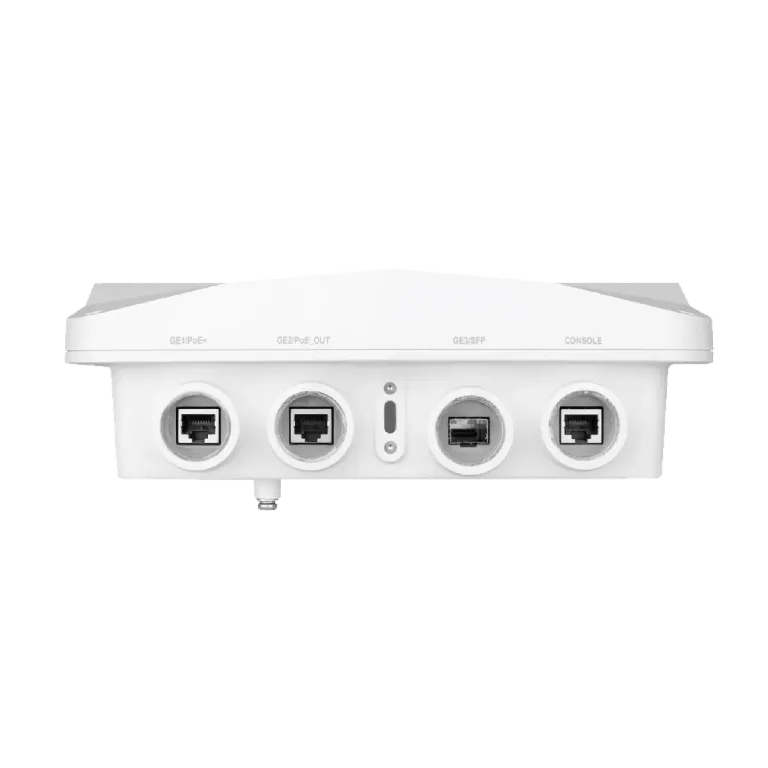
An outdoor Wi-Fi 6 AP with two 2x2 radios, switchable to dual 5 GHz, plus PoE-out for cameras or sensors.